Request info
Want to know more before you sign up?
Send a short question and we will forward it directly to the provider.
We forward your question to Newton. No spam, no third parties.
Send a short question and we will forward it directly to the provider.
We forward your question to Newton. No spam, no third parties.
YH02489
After completing the programme, the student shall have knowledge of/in - the background and purpose of the GDPR legislation and what it means for companies and organisations. - how to implement the legislation in practice in the business and organisation, and identify the differences in requirements and expectations that exist for different types of organisations. - what constitutes personal data in different situations and systems, and which professional roles handle them. - which rights data subjects have and how those rights should be responded to. - Privacy by Design and Privacy by Default. How systems are designed to protect personal data in order to comply with Article 25 GDPR. - the guidelines from ENISA (European Union Agency for Network and Information Security) and which requirements are placed on the development of systems, services and software. - design requirements for database models and business systems. - implementation of encryption for sensitive data and personal data, and methods and functions for anonymising sensitive information. - implementation of routines and automation for purging collected data, known as data clearance. And identifying when information needs to be purged and which intervals are suitable for different types of data. - methods and functions to ensure that data subjects can request erasure of collected data. After completing the programme, the student shall have skills in - explaining and reflecting on the parts of the GDPR legislation relevant to the company or organisation, such as which data may be collected and how it should be handled. - ensuring, based on data subjects' rights, that their requests to be erased from systems and registers are met. - analysing companies' and organisations' need for personal data in relation to the intentions of the legislation and setting requirements for systems and operations based on the analysis. - setting requirements for and developing systems for encryption, anonymisation and pseudonymisation independent of software. - designing and developing systems and software that ensure that unauthorised personal data and privacy-infringing material is not collected. - designing and developing systems and software that ensure that information is automatically purged and forgotten, through work with, for example, CI/CD tools. After completing the programme, the student shall have competences to - independently carry out analysis and mapping of their own company's or organisation's need to collect personal data and other individual-related data in relation to the GDPR legislation. - independently or in a team identify what their own company needs to develop or change in order to meet the requirements of GDPR and how the company's internal ongoing review work should be designed. - independently or in a team set relevant requirements for purging and encryption of personal data in the design of, for example, services, systems and apps. - independently design functional requirements for database models and business systems. - independently or in a team develop, for example, services, systems and apps with automated purging, and enable data subjects to have their data removed on request. - understand how GDPR interacts with and must be complied with when implementing artificial intelligence (AI) and other technology development.
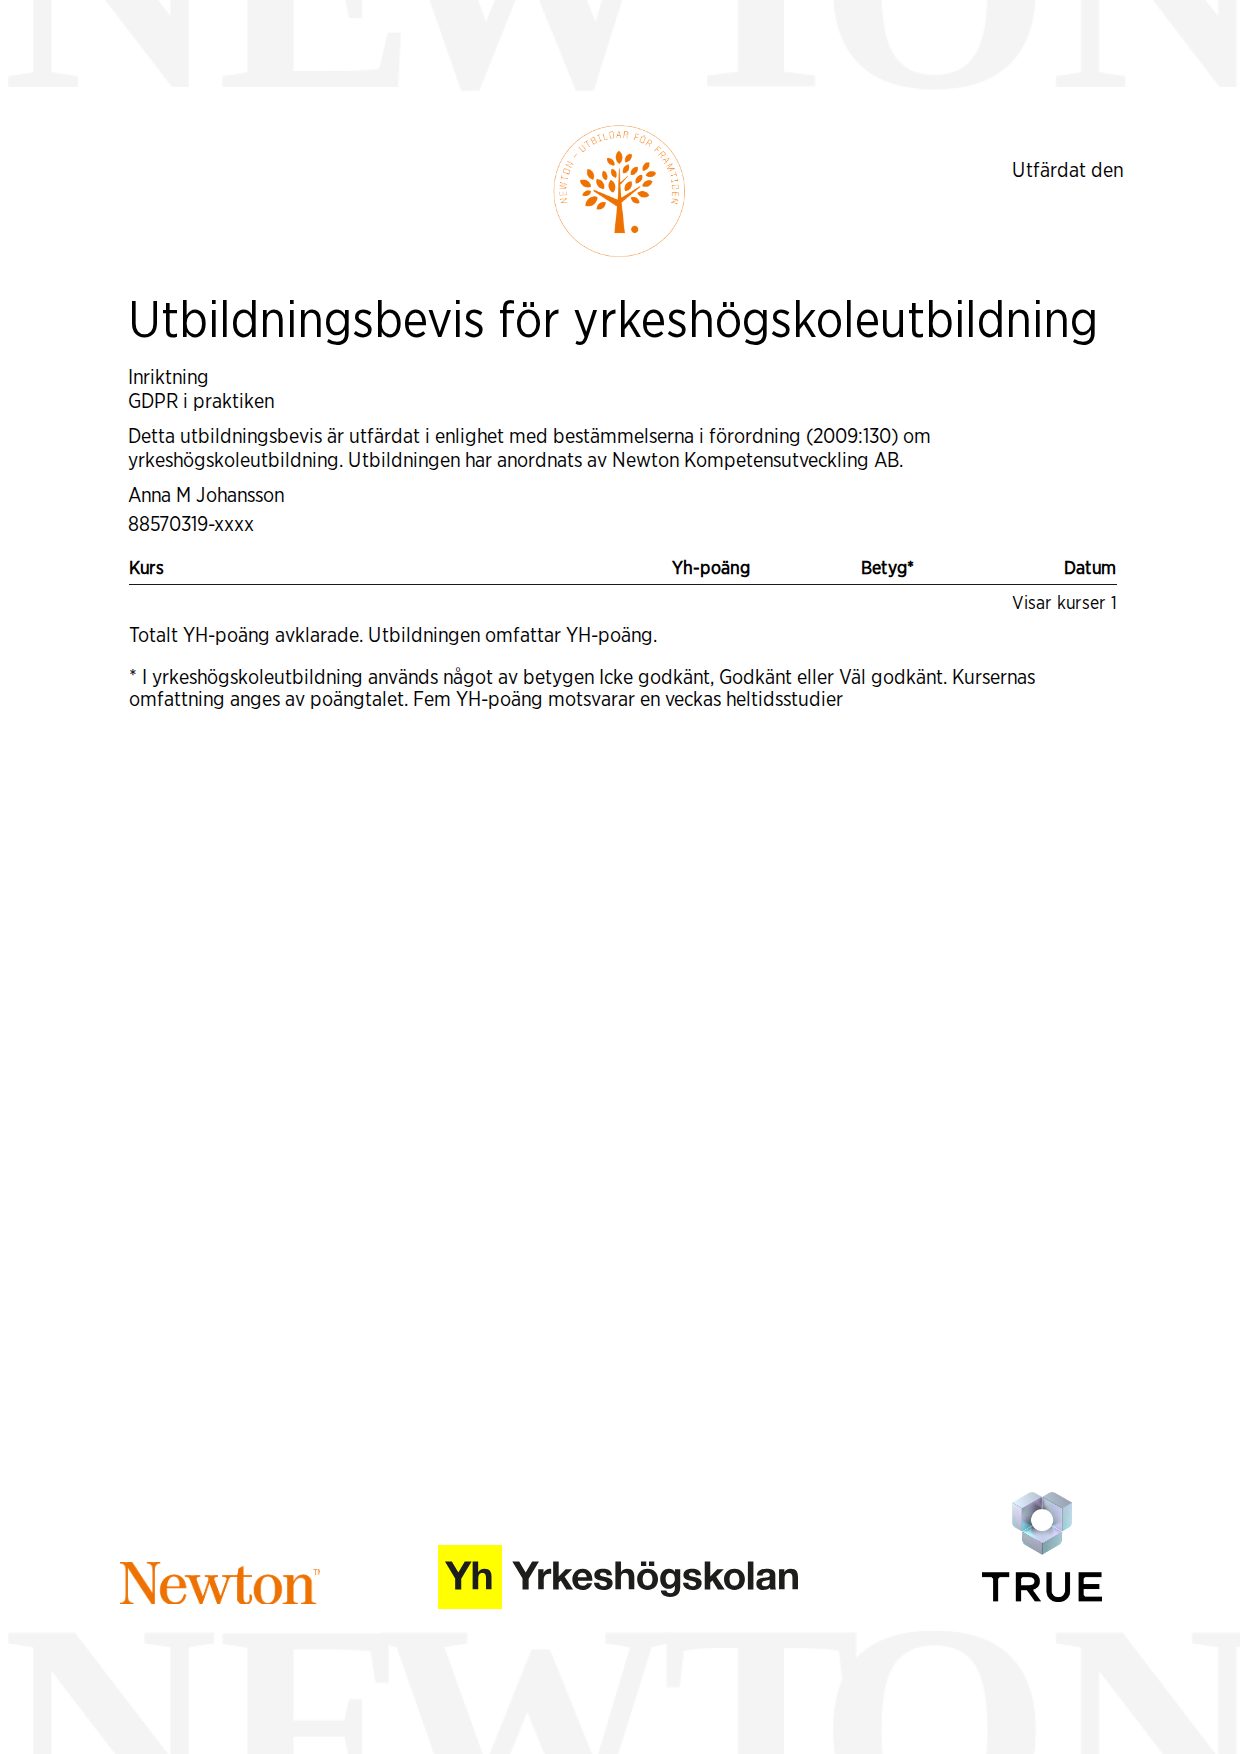
When you complete the course, Newton issues your certificate. Your name, the course content and the issue date are encrypted and secured on blockchain, so it cannot be changed, and anyone can check that it is genuine.
Sample Credential with placeholder data. Each credential is issued with the recipient’s details and is verifiable with the provider.