Part of a YH programme at TUC Yrkeshögskola. This course cannot be applied for on its own. Programme code: ITS19JÖN.
Security, Basics gives you knowledge of potential threats and risks in IT and of how to prevent and deal with a hacked site. You gain knowledge of which rules and systems are needed to protect the company against digital attacks, and learn basic techniques for unauthorised intrusion such as XSS, SQL injections, social engineering and brute force. After the course you can design a user policy and show the savings made when rules and routines are followed.
Duration: 4 weeks
Language: Swedish
Level: Beginner
CSN-eligible
Time commitment: 20 YH credits, about 4 weeks of full-time study
Course purpose and goals
The goal of the course is to give students in-depth knowledge of information and computer security and the impact the right security technology can have on society. The goal of the course is also to give students the knowledge to carry out digital investigation techniques and gain an understanding of the relationship between computer and human. After completing the course, students can act as advisers on security issues.
What you will learn
What you learn.
Has knowledge of potential threats and risks in IT security
Can prevent and deal with a hacked website
Knows basic attack techniques such as XSS, SQL injection, social engineering and brute force
Can design a user policy to reduce security risks
Understands how rules and routines reduce the risks and costs linked to IT security
Curriculum
How the course is built.
Threats and risks in IT
Common threats and risks that companies face in a digital environment.
Attack techniques
Basic techniques for unauthorised intrusion: XSS, SQL injection, social engineering and brute force.
Dealing with a hacked site
How to act when a website has been hacked.
User policy and routines
Designing rules and a user policy that reduce risks in the organisation.
Target audience
Who is this for?
The course is aimed at you who are new to IT security and want to understand basic threats, attack techniques and protection against digital attacks.
What "verified" means here
Verified credential.
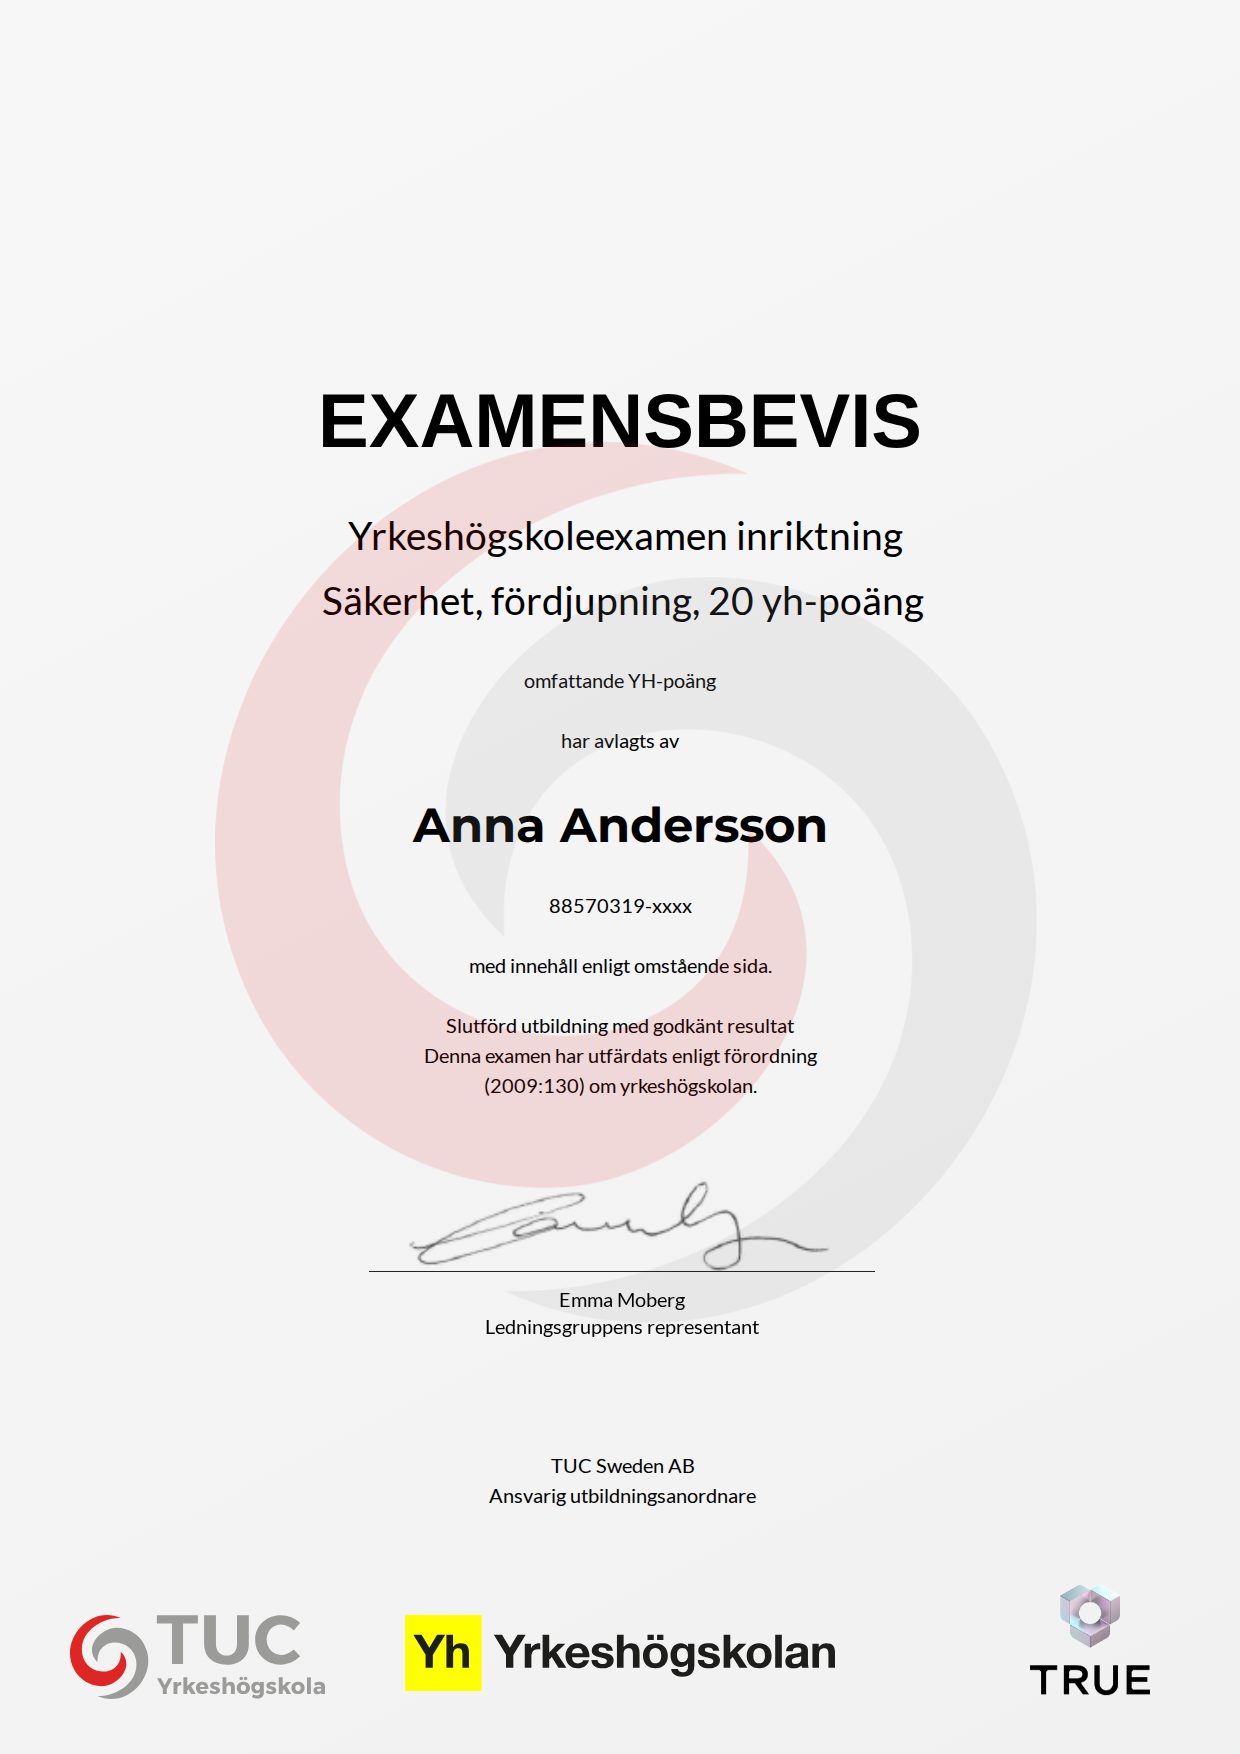
When you complete the course, TUC Yrkeshögskola issues your certificate. Your name, the course content and the issue date are encrypted and secured on blockchain, so it cannot be changed, and anyone can check that it is genuine.
100% Verifiable certificates Secured on blockchain