Network security 2 is an advanced course within Nackademin's YH programme in network and IT security. The course gives you in-depth knowledge of testing and strengthening security in networks, from physical security to the protection of computers and connected devices. You learn to recognise different types of malicious code and common attack methods against Linux, macOS and Windows, and how to implement preventive measures. There is a strong focus on practical work with monitoring, penetration testing and technical security tools.
Duration: 20 weeks
Format: Online
Language: Swedish
Level: Intermediate
CSN-eligible
Time commitment: Course module of 20 YH credits (equivalent to about four weeks of full-time study) within a two-year YH programme
Request info
Want to know more before you sign up?
Send a short question and we will forward it directly to the provider.
We forward your question to Nackademin. No spam, no third parties.
About the course.
Class: ITS19 Course: Network security 2 gives: 20 p
The purpose of the course is to give students in-depth knowledge of network security by testing security.
The goal of the course is that students will know the different types of malicious code that exist in order to implement preventive measures in networks.
The approved student has knowledge of
- Security risks in a network, from physical security to the security of the computer network and connected devices
- The most common attack methods used against Linux, macOS and Windows
- Methods used in intrusion attempts
- Automated network analysis (UEBA, SIEM)
- Technical aids and software available to prevent unauthorised access
- DLP (Data loss prevention software)
The approved student has the skills to
- Prevent intrusion attempts by implementing monitoring systems
- Test security by carrying out penetration tests
- Technically examine IT environments from a security perspective
The approved student has the competence to
- Work preventively with security in networks and operating systems
What you will learn
What you learn.
You know the security risks in a network, from physical security to the security of computers and connected devices.
You know the most common attack methods against Linux, macOS and Windows and the methods used in intrusion attempts.
You understand automated network analysis with UEBA and SIEM as well as DLP (Data Loss Prevention).
You can prevent intrusion attempts by implementing monitoring systems.
You can test security by carrying out penetration tests.
You can technically examine IT environments from a security perspective.
You have the competence to work preventively with security in networks and operating systems.
Curriculum
How the course is built.
Security risks in networks
From physical security to the security of computer networks and connected devices.
Attacks and malicious code
Common attack methods against Linux, macOS and Windows, different types of malicious code and preventive measures.
Intrusion methods and monitoring
Methods used in intrusion attempts and how monitoring systems are implemented to prevent them.
Automated network analysis
UEBA, SIEM and DLP (Data Loss Prevention) to detect and prevent unauthorised access.
Penetration testing
Practical security testing through penetration tests and technical examination of IT environments.
Target audience
Who is this for?
Students in Nackademin's YH programme in network and IT security who want to specialise in network security, threat detection and penetration testing. Aimed at future IT security technicians.
What "verified" means here
Verified credential.
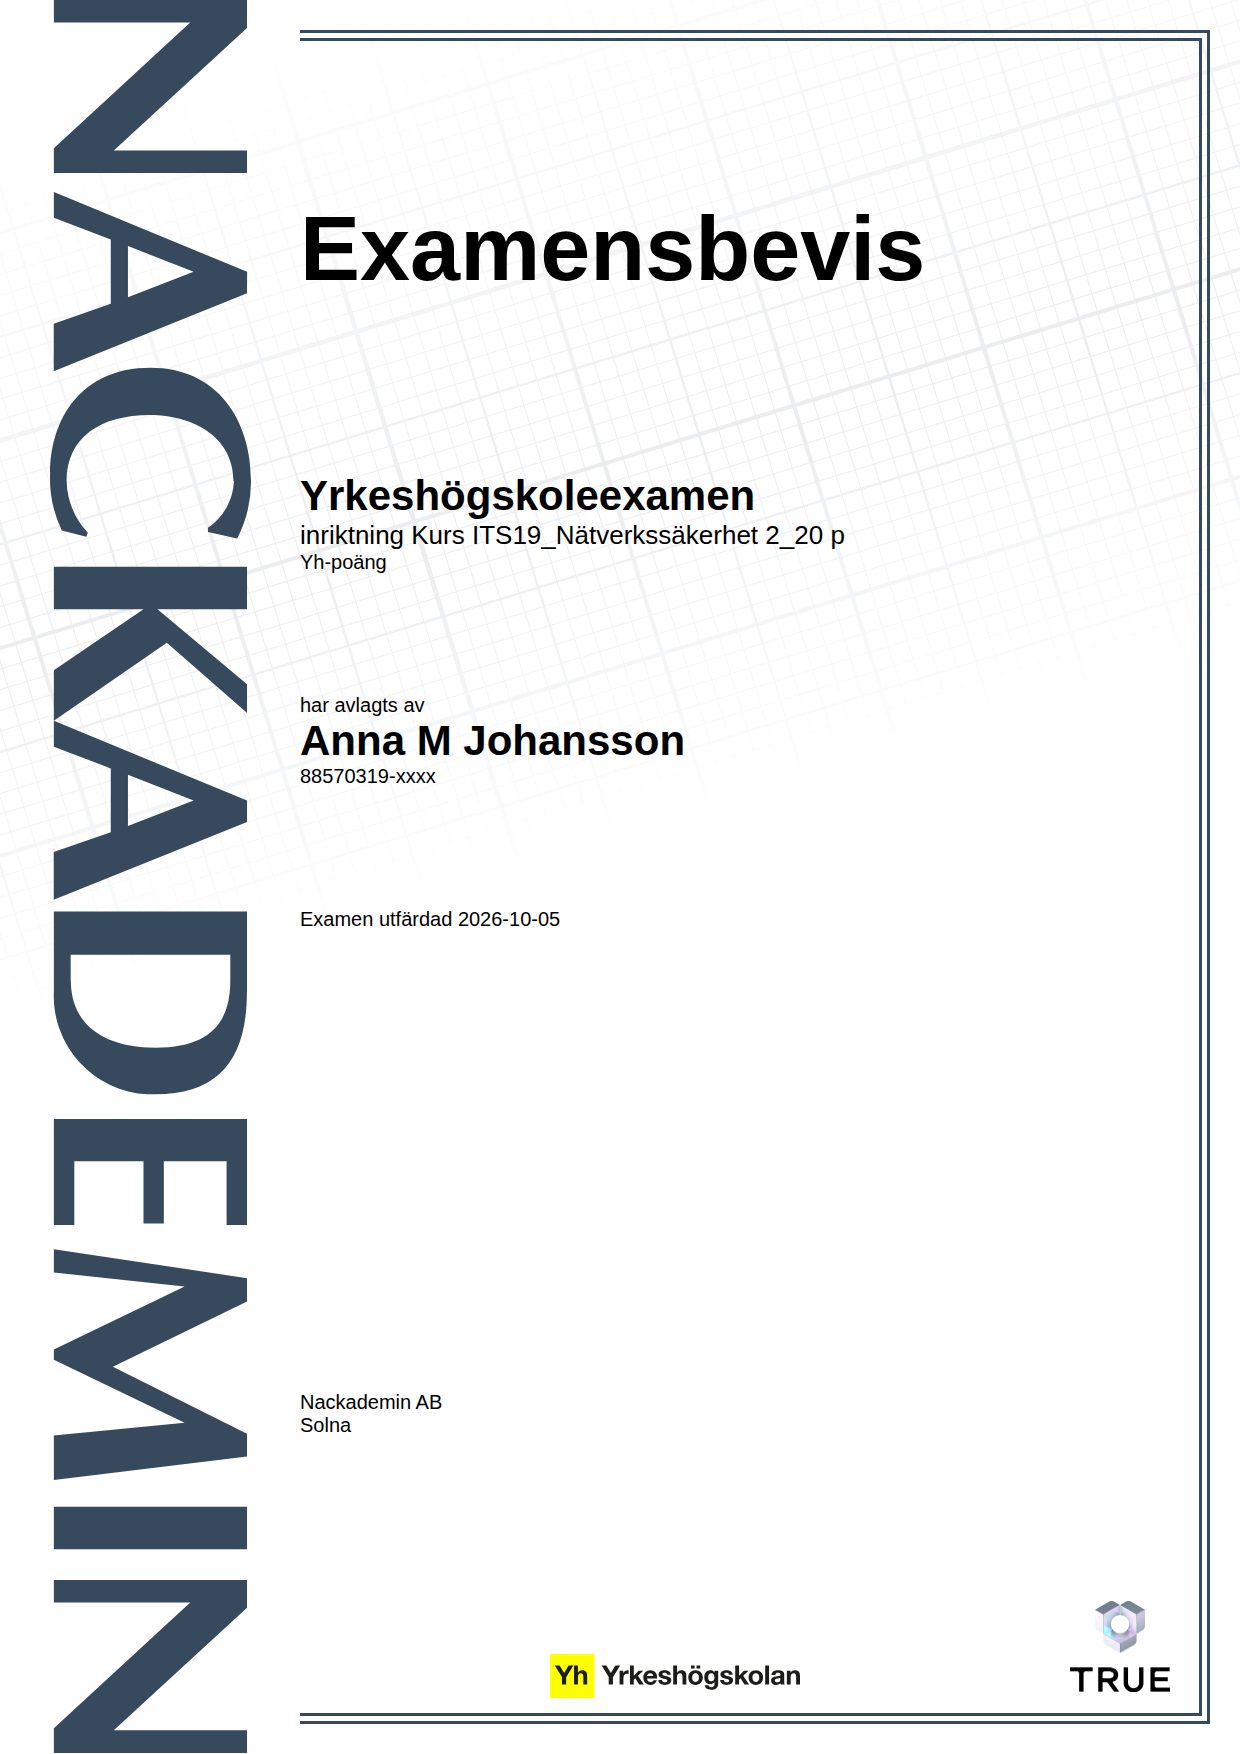
When you complete the course, Nackademin issues your certificate. Your name, the course content and the issue date are encrypted and secured on blockchain, so it cannot be changed, and anyone can check that it is genuine.
100% Verifiable certificates Secured on blockchain