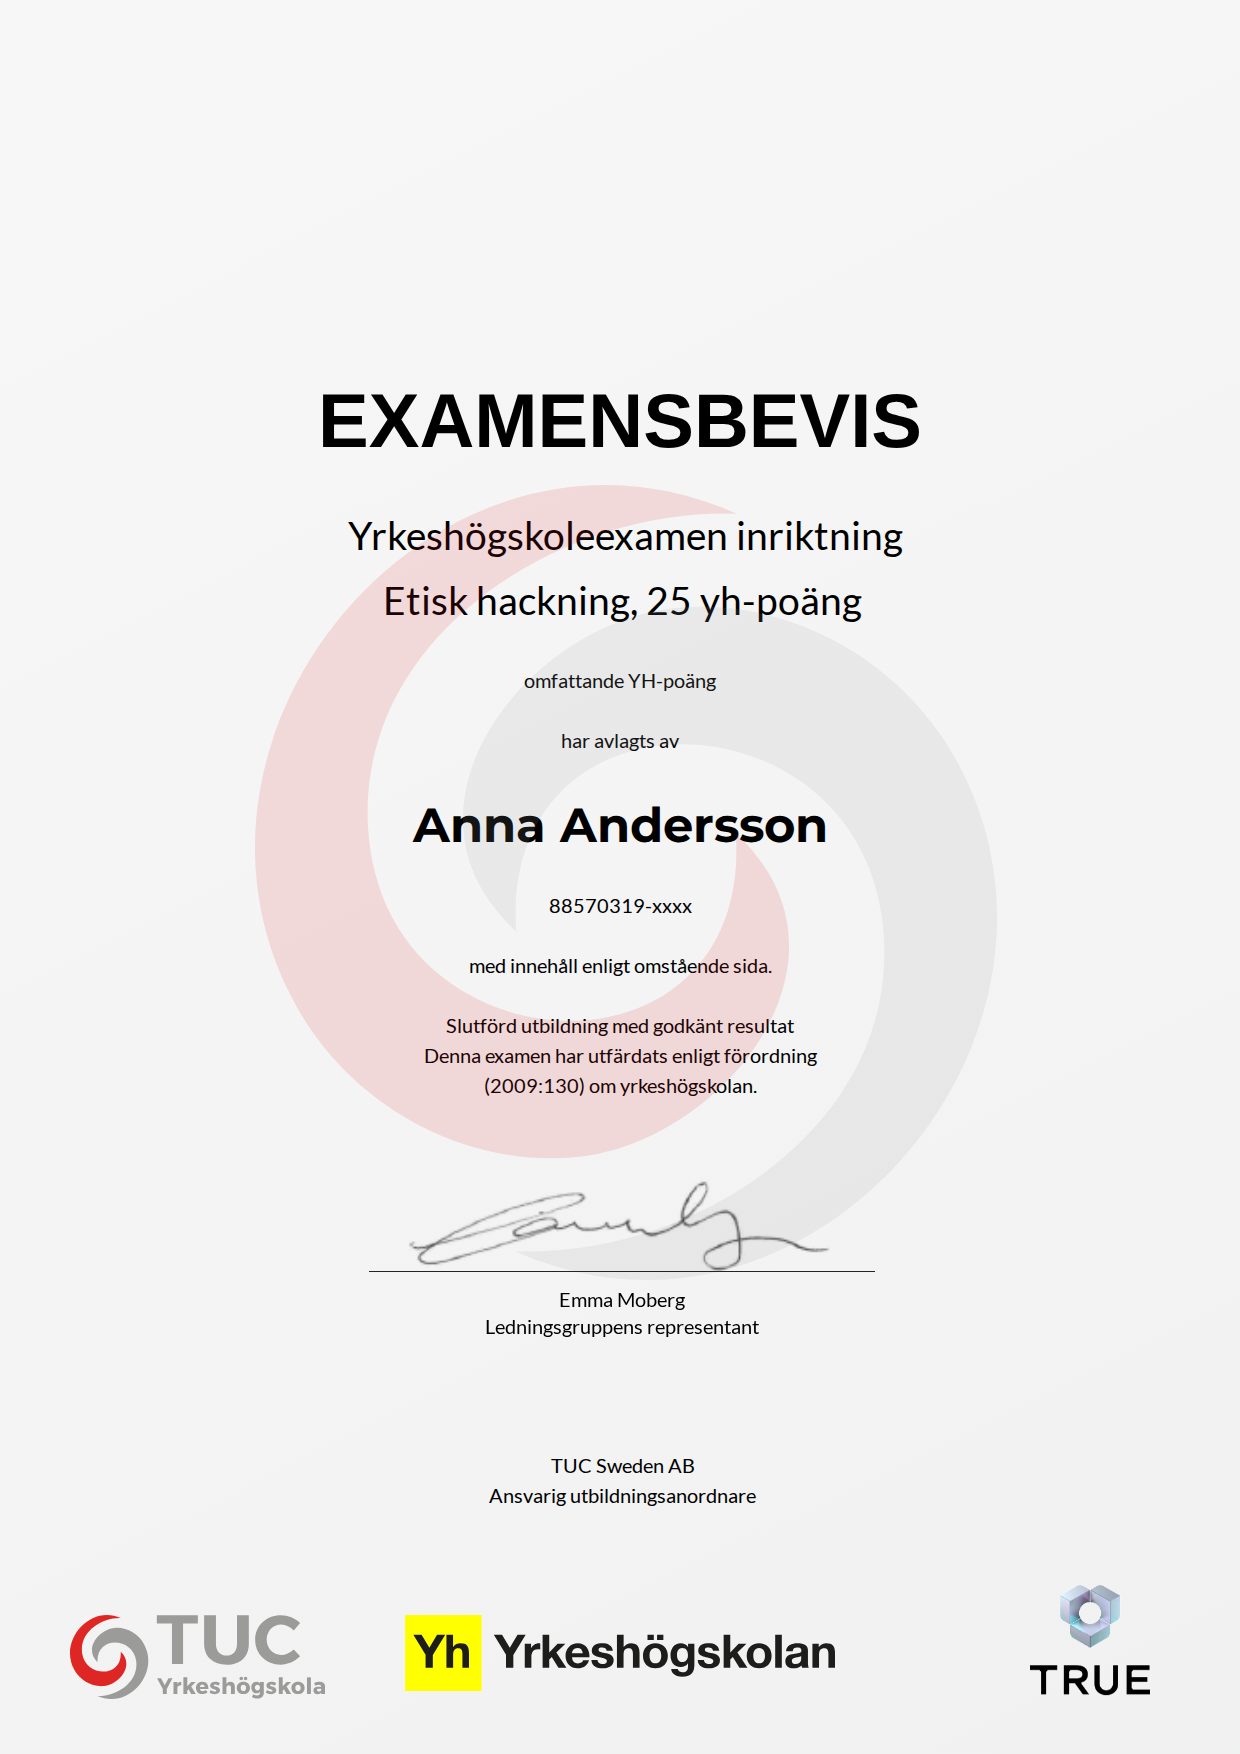
Part of a YH programme at TUC Yrkeshögskola. This course cannot be applied for on its own. Programme code: ITS19JÖN.
Ethical Hacking, 25 YH credits, teaches you to analyse hardware-based vulnerabilities and protection mechanisms in an IT infrastructure and to carry out authorised intrusion attempts. You gain knowledge of monitoring and intrusion detection strategies, reconnaissance techniques, incident handling and securing evidence after an incident. The course is part of TUC's YH programme for IT security specialists and includes several lab exercises.
Duration: 25 h
Language: Swedish
Level: Advanced
CSN-eligible
Time commitment: Full-time study equivalent to 25 YH credits (approx. 5 weeks)
Course purpose and goals
The goal of the course is to give students in-depth knowledge so that they can find security gaps in a system and in a company's IT environment. The course also aims to give students tools and methods for attacking a target and finding attack vectors for hacking. After completing the course, the student should be better able to protect companies against intrusion. This is done by giving students an understanding of how a hacker thinks and acts.
What you will learn
What you learn.
You can analyse hardware-based vulnerabilities and protection mechanisms in an IT infrastructure.
You can carry out authorised attempts to break into IT infrastructures under controlled conditions.
You can justify the use of different monitoring and intrusion detection strategies.
You have knowledge of reconnaissance techniques and types of attack.
You can handle incidents, restore systems and secure evidence after an attack.
Curriculum
How the course is built.
Vulnerability analysis
Analysis of hardware-based vulnerabilities in IT infrastructure.
Authorised penetration testing
Practical exercises in ethical hacking under controlled conditions.
Monitoring and intrusion detection
Strategies for monitoring and detecting intrusions.
Incident handling
Handling, restoring and securing evidence after a security incident.
Lab exercises
Practical exercises and lab work across all parts of the course.
Target audience
Who is this for?
The course is aimed at YH students training to become IT security specialists.
What "verified" means here
Verified credential.
When you complete the course, TUC Yrkeshögskola issues your certificate. Your name, the course content and the issue date are encrypted and secured on blockchain, so it cannot be changed, and anyone can check that it is genuine.
100% Verifiable certificates Secured on blockchain