The Cyber Resilience Act (CRA) is an EU regulation that sets cybersecurity requirements for products with digital and connected elements. During this training day at IFI you gain in-depth knowledge of the regulation's content, its application and what it means in practice for manufacturers and suppliers. You also learn how the CRA relates to the Cybersecurity Act (CSA) and NIS2, and which certifications and standards are emerging. The course is held in hybrid format: on site in Stockholm or online.
Duration: 1 day
Format: Hybrid
Location: Stockholm
Language: Swedish
Level: Intermediate
Time commitment: 1 full day, 09:00-16:00
Request info
Want to know more before you sign up?
Send a short question and we will forward it directly to the provider.
We forward your question to IFI AB. No spam, no third parties.
About the course.
EU regulation focused on cybersecurity requirements for products with digital and connected elements.
What you will learn
What you learn.
You understand the content and scope of the Cyber Resilience Act
You can explain the links between the CRA, the Cybersecurity Act (CSA) and NIS2
You know the manufacturer's obligations regarding cybersecurity assessment of products
You know how product life cycle and security are to be handled under the regulation
You understand the reporting obligations when vulnerabilities are discovered
You know the rules for market surveillance
You are aware of new certifications and standards in cybersecurity
You know the timetable for the regulation's implementation
Curriculum
How the course is built.
Cyber Resilience Act: content and application
A review of the regulation's content, scope and practical application.
Links to CSA and NIS2
How the CRA relates to other regulations such as the Cybersecurity Act and NIS2.
Manufacturer obligations
Requirements for cybersecurity assessment and risk management throughout the product life cycle.
Reporting vulnerabilities
Obligations to report discovered vulnerabilities to the relevant authorities.
Market surveillance
Rules for market surveillance and supervision of products with digital elements.
Certification and standards
Upcoming certification frameworks, relevant standards and the implementation timetable.
Target audience
Who is this for?
The course is aimed at you who work with product development, regulatory compliance, procurement or cybersecurity and want to understand the practical consequences of the Cyber Resilience Act for your organisation.
What "verified" means here
Verified credential.
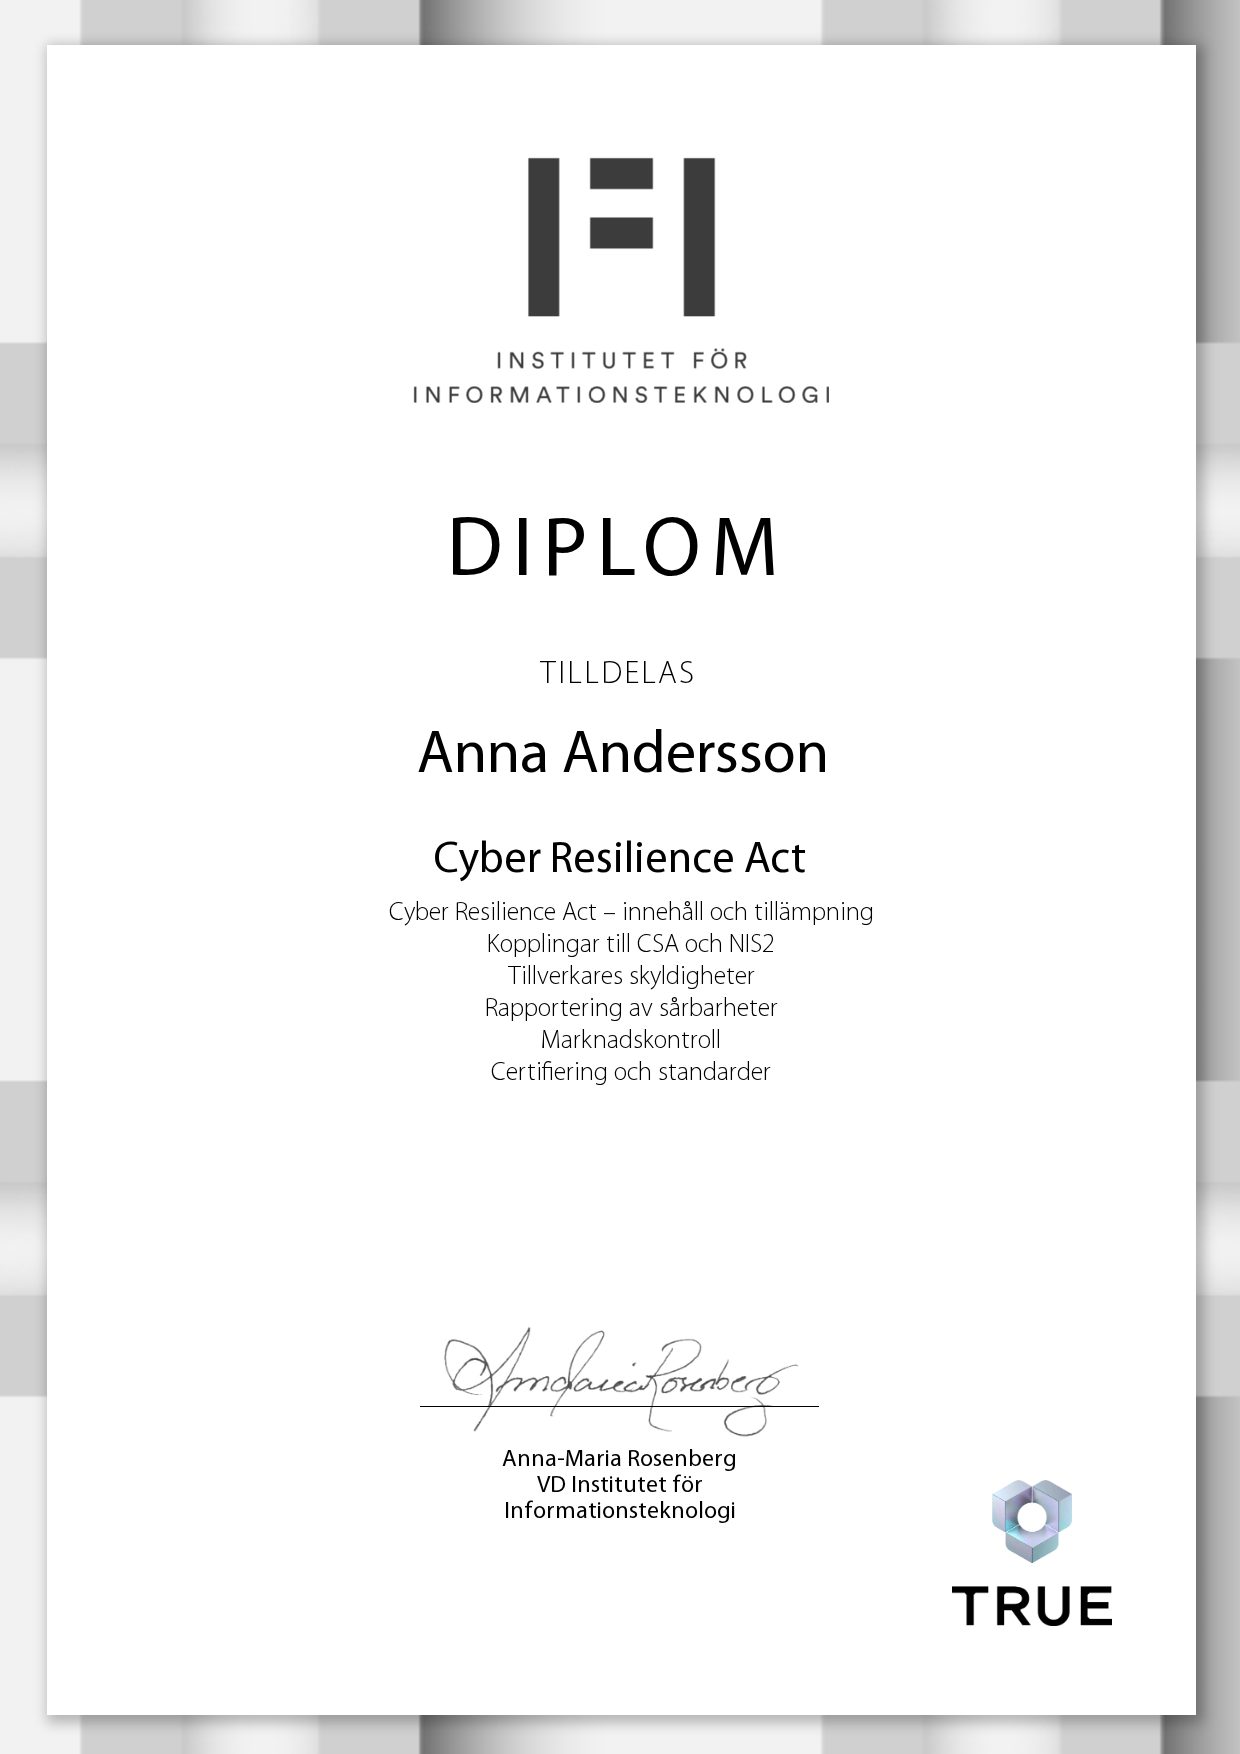
When you complete the course, IFI AB issues your certificate. Your name, the course content and the issue date are encrypted and secured on blockchain, so it cannot be changed, and anyone can check that it is genuine.
Dozens of credentials issued 100% Verifiable certificates Secured on blockchain